A customer wants your SOC 2 report before they sign.
Compliance landed on your desk on top of everything else. A customer sends a questionnaire, a payments partner needs PCI DSS, a healthcare buyer needs HIPAA, and the requirements keep changing. An ineffective program, policies copied from a template and a tool nobody has time to run, costs growing tech companies opportunities and customer trust. It should not be the thing that slows your company down.
Expert-led. Technology-powered.
Every engagement is led by senior GRC experts who run the program alongside your team.
Virtual Compliance Management
We join your team and run your entire compliance program year-round, so your engineers keep building and you walk into every security review ready.
Assessment & Readiness
Know exactly where you stand before committing to an audit. Our readiness assessments map your current security posture against target frameworks and deliver a prioritized remediation roadmap.
Information Security Risk Assessment
Rigorous risk identification and analysis aligned to your business context. We deliver a risk register that maps to your actual threat landscape and informs your control priorities.
ISO Internal Audit
Independent internal audits to satisfy ISO 27001 and ISO 42001 certification requirements. We identify nonconformities before your certification body does.
Your Security and Compliance Roadmap.
Whether you're pursuing your first SOC 2 or expanding into ISO 27001, we build your program in the first 60 to 120 days, run it all year, and keep you ready.
Discovery & Scoping
We assess your current security posture, understand your business context, and define scope. No cookie-cutter approaches. Every engagement starts with your reality.
Program Design
We design your control framework, map it to target standards, build your policy library, and configure tooling to match your organization's workflows.
Implementation & Evidence
We work alongside your team to implement controls, establish evidence collection, and conduct training to make compliance part of daily operations.
Audit & Continuous Management
We prepare you for audit and manage the audit with your auditor from kickoff to final report. Then we keep the program running all year, keeping controls current, collecting evidence, and evolving your program.
Part of the team behind your compliance program.
Real practitioners. Real relationships. Every engagement is led by senior consultants who stay with you from kickoff through audit and beyond.
Meet the Team →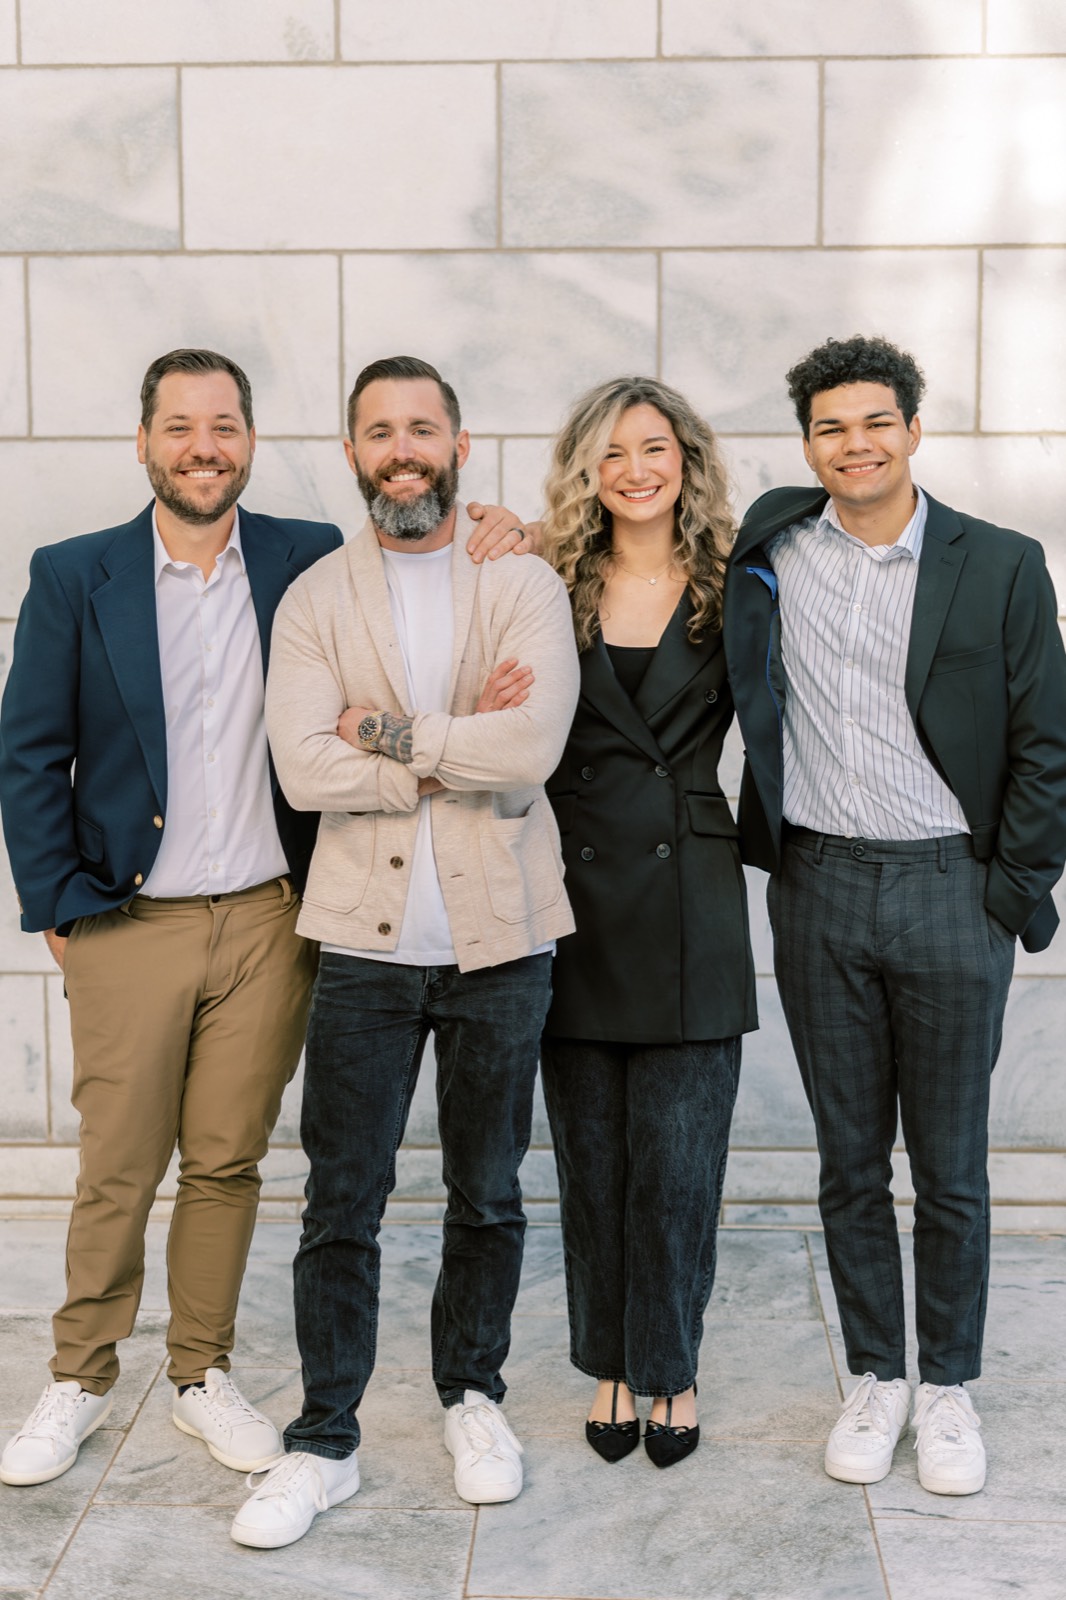
What makes us different.
You work with senior GRC experts who know your program inside and out, and most people on our clients' teams come to see us as part of their own team.
GRC Experts, Not a Factory
You work directly with senior GRC experts who know your program inside and out. The same senior team stays on your account year after year. No junior analysts, no revolving doors.
Technology + People
Every engagement combines the ConcertoGRC platform with a dedicated senior team, so you get the tools and the people together as one program, included in the work.
Cloud-Native Expertise
We understand modern architectures, fast-moving teams, and the balance between security maturity and business velocity. Whether you're standing up your first program or scaling an existing one, we meet you where you are.
Continuous, Not Point-in-Time
Compliance isn't a project with an end date. We run your program all year, keeping controls current, collecting evidence, and keeping you audit-ready every day.
People and platform, together.
ConcertoGRC is the platform we run your program on, included with every Virtual Compliance Management engagement. Framework controls, evidence, risk, vendors, and policies live in one place, so you don't need Vanta or Drata, or a separate security awareness training provider like KnowBe4.
You get the tools and the team as one program, run by the same senior people year after year.
Explore the platformConcerto Compliance has proven to be a great partner in helping us implement and manage our security compliance program. They understand cloud-based technology and have helped us bridge the gap between our security compliance requirements and business objectives. I've never met a team who could make compliance as easy, and dare I say FUN!
Enterprise compliance. SMB budget.
Building an in-house compliance function is expensive. A compliance manager, GRC platform, audits, and external consultants can easily exceed $250K per year. Concerto gives you all of it, bundled into a service that costs a fraction.
Grow confidently. Close your biggest deals.
Schedule a free consultation with Glenn Chamberlain, Managing Principal. We'll map out your compliance gaps, recommend a framework, and show you exactly what the path to audit-ready looks like.